Thousands of sources. Dozens of formats. Different languages, schemas and update schedules. The world's risk intelligence data was never built to work together, until now.
Risk intelligence doesn't fail because it's hard to read. It fails because the data underneath it was never built to connect. Sources that don't know about each other. Formats that can't speak to each other. Updates on different cycles, governed by different standards, in different languages.
Watchlist data. Adverse media. Corporate registries. Court records. Each built independently, with no intention of ever connecting to the others.
Structured SQL. Unstructured web text. Government XML. PDFs. Each source speaks a different data language, with no shared schema, identifier or format.
Each source updates on its own schedule. A risk surfacing today may not appear in your tools until tomorrow, or next week. Regulators don't wait.
Building a proprietary data intelligence layer sounds logical, until you meet the true scale of what it requires. The organisations that have tried know: this is not a data pipeline problem. It is a decade-long infrastructure challenge.
In-house data projects rarely finish. Regulatory requirements shift. Sources go dark. Maintenance never ends.
Data licensing. AI engineers. Legal review. Infrastructure. The hidden costs dwarf the build, and most discover this too late.
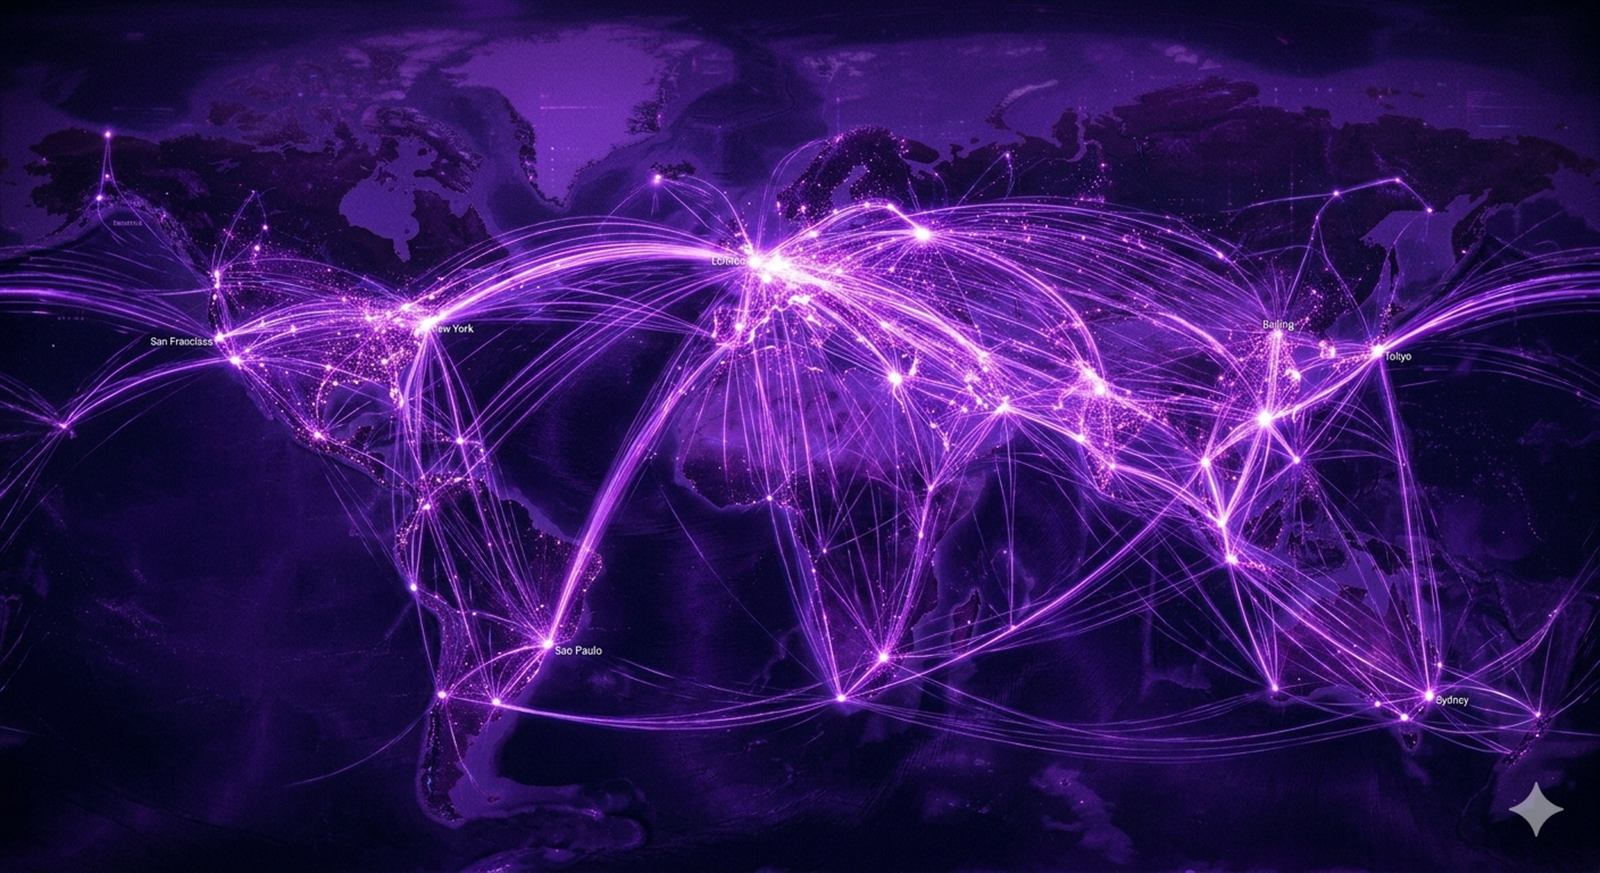
No team covers 15,000+ sources across 200 jurisdictions. In compliance, the source you're missing is the one that matters.
We don't just aggregate data. We ingest it, normalise it, resolve identities across sources, enrich it with context and synthesise it into intelligence your compliance team can act on, and your auditors can defend.
15,000+ sources
One unified language
AI cross-matching
Context layered
Risk signals surfaced
Audit-ready output
Aggregation is easy. Anyone can pull a list. The hard problem, the one that actually protects your organisation, is determining that “J. Smith, Board Member, ABC (Pty) Ltd” and “John Andrew Smith, Director, ABC Holdings International” are the same person. Our AI resolves this at scale, across thousands of sources, in milliseconds.
Matching across registries with no shared identifiers.
Name variants, transliterations and aliases, caught every time.
Every match scored, not binary. Defensible in audit.

Across watchlists, registries, unstructured media, courts and ESG data
Eight distinct source categories, each continuously monitored, normalised and enriched by our intelligence infrastructure.
OFAC, UN Security Council, EU, UK HMT/OFSI, FIC, INTERPOL and 44+ more databases, continuously updated across all major jurisdictions.
Global and regional PEP registries covering heads of state, government officials and their immediate associates.
Company registration, beneficial ownership structures and directorship records from official registries across 200+ jurisdictions.
Tens of millions of articles, reports and publications, parsed, deduplicated and scored for credibility and relevance across languages and regions.
Civil and criminal court filings, judgments and ongoing litigation from global legal databases and official court records.
Environmental controversies, social violations and governance failures from international ESG ratings and investigative reporting.
Fines, debarments and enforcement filings from regulators across FATF member states and beyond.
Official blacklists, debarment registers and enforcement actions from government authorities across 200+ jurisdictions.
From major financial centres to high-risk corridors, with particular depth across Africa, the FATF grey-list landscape and emerging-market jurisdictions where off-the-shelf solutions consistently fall short.

A risk that emerged this morning should appear in your next screening, not in next month's batch update. Our infrastructure runs continuous ingestion cycles so your intelligence reflects the current state of the world, not yesterday's snapshot.
Our data infrastructure took years to build and never stops evolving. Speak with one of our experts: no pitch, just clarity on what it means for your compliance programme.